
The Governance Gap: Why AI Policies Alone Cannot Protect a Law Firm
Six pillars for turning professional responsibility into operational accountability across law firm AI use.
Imagine a managing partner discovering that several attorneys in the firm are already using different artificial intelligence platforms to conduct legal research, draft documents, and summarize client records.
A paralegal has been experimenting with a consumer AI application. The intake team has introduced an automated assistant. Another vendor recently added AI functionality to software the firm has used for years.
Each tool may offer legitimate benefits. Attorneys can retrieve information more efficiently, accelerate routine work, and devote greater attention to matters requiring professional judgment.
But who approved these systems?
Does anyone know which applications receive confidential client information? Who reviews their outputs? Which vendors retain uploaded material? What happens when an AI-generated answer is wrong, or an employee uses an unapproved system?
The firm may have policies covering technology and confidentiality. It may even have circulated an internal memorandum warning lawyers not to upload sensitive information into public AI tools.
Yet no one has established an integrated process for governing artificial intelligence across the practice.
That is the problem I describe in my continuing legal education programs as the Governance Gap.
“The real problem isn’t AI adoption. It’s unmanaged adoption.”
Jeff Howell, Esq. | Lex Wire Journal
The distinction is important. Artificial intelligence is not inherently incompatible with responsible legal practice. But when adoption occurs without clear responsibility, appropriate safeguards, and consistent review, firms create risks they may not even recognize.
Effective governance is the system that turns professional responsibilities into rules and procedures people can actually follow.
The Bottom Line
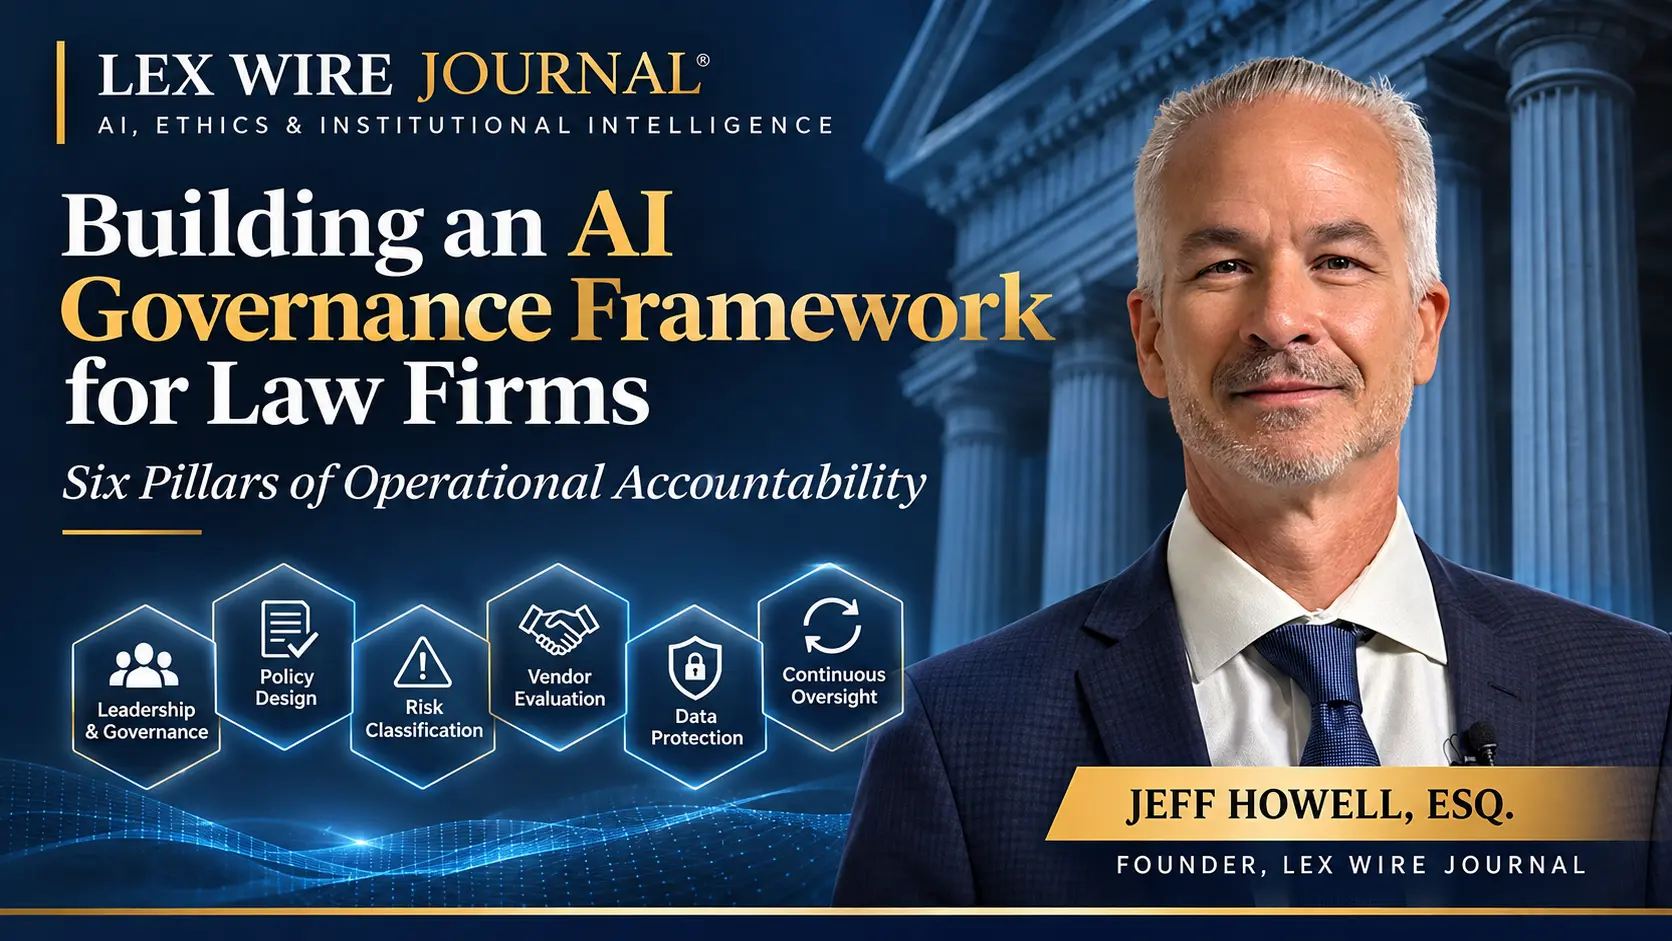
Law firm AI governance requires more than a written policy or a list of approved technology providers. It requires a coordinated framework covering leadership, policy design, risk classification, vendor evaluation, data protection, and continuous oversight. These six pillars provide a practical structure for governing AI use while preserving professional judgment and supporting responsible innovation.
From Individual Experimentation to Institutional Responsibility
Historically, law firms have governed technology through a combination of information security policies, professional supervision, vendor agreements, and internal operating procedures.
These systems remain necessary, but AI introduces a distinctive challenge: the same technology may perform very different functions, process different categories of information, and produce outputs with very different consequences.
A lawyer might use a general-purpose AI assistant to organize a personal task list in the morning, summarize a deposition in the afternoon, and evaluate a potential litigation strategy before leaving the office.
The technology may be similar. The professional risks are not.
AI functionality is also increasingly embedded inside existing software. An employee may begin using an AI feature without recognizing that information handling practices have changed.
This creates several governance problems.
First, visibility. Firm leadership cannot govern systems it does not know are in use. Informal experimentation, sometimes described as shadow AI, may bypass ordinary approval procedures.
Second, fragmented responsibility. Technology personnel may understand security, partners may understand client obligations, and vendors may understand their own products. But responsibility for evaluating the complete workflow may be unclear.
Third, inconsistent oversight. One practice group may carefully review and document AI-assisted work while another relies on informal assumptions about accuracy.
Fourth, policies disconnected from practice. A general instruction to use AI responsibly does not tell an associate which tool is approved, which information may be entered, or when partner review is necessary.
The result can be a law firm that recognizes the importance of ethical AI use without having a reliable way to manage it.
The American Bar Association addressed the ethical implications of generative AI in Formal Opinion 512, Generative Artificial Intelligence Tools , issued July 29, 2024.
The opinion examines familiar duties involving competence, confidentiality, communication, supervision, candor, meritorious claims, and reasonable fees.
Those duties are not replaced by a new technology. They must be applied to the circumstances in which that technology is used.
Importantly, ABA Model Rules are not automatically the governing disciplinary rules in every jurisdiction. Firms must evaluate applicable state rules, ethics opinions, court requirements, and client obligations.
That is precisely why governance must become an ongoing organizational function rather than a one-time response to a new product.
The Six Pillars of Law Firm AI Governance
In my AI governance CLE programs for the National Academy of Continuing Legal Education and Lawline, I organize the governance process around six interconnected pillars.
They provide a practical framework for turning abstract professional obligations into identifiable responsibilities, documented procedures, and repeatable decisions.
These pillars are interdependent. Vendor approval accomplishes little without rules governing how the approved product may be used. A confidentiality policy is incomplete without training and oversight. Monitoring will be ineffective unless someone has responsibility for responding to what it reveals.
The framework is designed to connect those functions without assuming every law firm requires an elaborate compliance department.
Pillar 1: Leadership and Governance Structure
Every law firm needs someone responsible for governing AI use.
That does not mean every firm needs a formal committee, expensive consultants, or several layers of management approval.
It means decisions must have identifiable owners.
In a larger firm, an AI governance committee might include representatives from practice leadership, IT, risk management, compliance, and operations.
A smaller firm might assign responsibility to a managing attorney supported by qualified outside technical advisers.
The important functions remain substantially the same:
- Approving or rejecting proposed AI systems.
- Establishing acceptable uses and restrictions.
- Assigning appropriate review responsibilities.
- Evaluating significant risks and exceptions.
- Monitoring incidents, vendor changes, and policy compliance.
- Ensuring identified problems are addressed.
Consider a litigation partner who wants to deploy a new AI document-review application.
The governance process should identify who evaluates the vendor, who assesses confidentiality obligations, which workflows are authorized, and what review must occur before work product is relied upon.
Without assigned responsibility, each person may reasonably assume someone else has completed the necessary evaluation.
That is how organizational gaps become professional risks.
My central recommendation is simple: make responsibility explicit before making the technology available.
Pillar 2: Policy Design and Scope
Once leadership responsibility is established, the next step is defining what responsible AI use means inside the firm.
The policy should not simply restate the Model Rules or reproduce a vendor’s security documentation.
Its purpose is to provide instructions that attorneys and staff can apply during ordinary work.
In my governance programs, I reduce policy design to three fundamental questions:
- What can we use? Identify approved tools and permitted purposes.
- How can we use it? Establish data handling, review, documentation, and workflow requirements.
- Who reviews it before it goes out the door? Assign accountability for work that reaches clients, courts, counterparties, or other external recipients.
The policy should address both technology selection and the actual uses of approved technology.
For example, a general AI assistant may be approved for drafting internal administrative material but prohibited from processing identifiable client information without additional authorization.
A specialized legal research platform may be approved for research assistance, while requiring attorneys to review the underlying authorities before relying on its conclusions.
The policy also needs procedures for reporting mistakes, requesting exceptions, and responding when an employee encounters a situation not already addressed.
“Your AI policy must be written in plain English.”
Jeff Howell, Esq. | Lex Wire Journal
An impressive policy that no one understands or follows provides little operational value.
Policies should be integrated into existing security procedures, engagement processes, staff training, and legal work protocols.
They should also be revised as tools, risks, and professional guidance change.
For firms looking for a concise practical companion, Lex Wire’s earlier article, Building Your Law Firm’s AI Playbook , addresses how policies and procedures can be organized for everyday use.
The broader governance framework, however, must extend beyond the existence of a written playbook.
Pillar 3: Risk Classification
Not all AI use presents the same level of risk, and not all applications should require the same approval process.
A uniform approach can create two problems.
If every AI activity requires exhaustive evaluation, employees may avoid the formal process or become frustrated by unnecessary administrative delays.
If every activity receives minimal review, the firm may fail to distinguish routine administrative tasks from work that could materially affect client rights.
The solution is risk-based classification.
My governance model uses three primary tiers: low, moderate, and high risk.
| Risk Level | Illustrative Uses | Governance Response |
|---|---|---|
| Low | Administrative scheduling, formatting, or general content work without sensitive client information. | Approved uses, standard safeguards, awareness, and periodic review. |
| Moderate | Internal drafting, document summarization, or research support where risks are controlled and outputs receive review. | Documented verification, suitable access controls, and assigned human responsibility. |
| High | Consequential legal analysis, sensitive information processing, or automated actions with significant client impact. | Enhanced assessment, approval, restrictions, documented supervision, and appropriate escalation. |
These categories are a proposed law firm governance method, not classifications mandated by the ABA Model Rules.
Their purpose is to help firms apply proportional safeguards.
The critical distinction is that risk belongs to the particular use and its information environment, not merely to the name of the AI product.
Consider three hypothetical situations involving a paralegal.
In the first, the paralegal uses AI to generate a general administrative checklist containing no confidential or sensitive information. That may be a low-risk application.
In the second, the paralegal uses an approved internal tool to summarize an authorized document, with controls restricting access and an attorney reviewing the results.
Depending on the document and its importance, that use may fall into a moderate-risk category.
In the third, the paralegal uploads confidential client records to an unapproved external AI service without understanding the provider’s data handling terms.
The exposure is materially different. That use could warrant a high-risk classification and immediate review.
The same employee may be using similar technology, but the information, authorization, and consequences have changed.
Classification should therefore consider several dimensions together:
- Information sensitivity: What client, personal, proprietary, or otherwise restricted information is involved?
- Consequences: What could happen if the output is wrong, incomplete, biased, or misleading?
- Human oversight: Who evaluates the result, and what expertise is required?
- System autonomy: Does the application merely suggest content or independently perform actions?
- Vendor exposure: Where is information processed, stored, retained, and potentially accessed?
A document-review task should not automatically be classified as moderate risk simply because someone plans to look at the output.
If it involves a major client decision, privileged information, or a consequential filing deadline, enhanced supervision may be necessary.
Risk classification should help the firm reach better decisions, not create a false sense of security.
Pillar 4: Vendor and Tool Evaluation
Most law firms will continue to rely on third-party providers for significant portions of their AI capabilities.
That makes vendor evaluation a core governance function.
A technology provider’s marketing materials are not a substitute for understanding the product’s actual behavior and contractual obligations.
Statements such as “enterprise-grade security,” “private AI,” or “compliant platform” may describe useful capabilities, but the firm still needs to determine what those claims mean in practice.
In my governance CLEs, I describe the Lex Wire Vendor Due Diligence Questionnaire as a structured way to organize that investigation.
It addresses five principal areas.
- Data security. Where is information stored and processed? What encryption, access controls, and security procedures are in place?
- Compliance and verification. Which security attestations or certifications are claimed, what do they actually cover, and what evidence can the vendor provide?
- Professional responsibility. How does the application handle confidentiality, retention, permissions, audit records, and information related to legal representation?
- Technical capabilities. What are the tool’s limitations, integration requirements, reliability, available safeguards, and export functions?
- Support and incident response. What happens when the system fails, information is exposed, or the firm needs urgent assistance?
A meaningful assessment should also examine whether information can be used to train or improve models, whether subprocessors have access, how long information is retained, and what deletion rights the firm possesses.
Contractual terms matter, but their significance depends on whether they correspond to the vendor’s technical and operational practices.
For example, a vendor might claim to maintain a recognized security attestation. The firm should determine which services are within its scope and whether the available evidence supports the representation.
An attestation does not independently determine whether a particular workflow satisfies attorney-client privilege requirements or the applicable ethical duties.
Similarly, an enterprise license does not automatically make every use of the product appropriate.
The firm’s responsibilities continue after purchasing the application.
Vendor terms, features, integrations, and data practices may change. Material changes should trigger renewed evaluation where appropriate.
The essential governance lesson is that approval should be based on a documented understanding of the relevant risks and safeguards, not simply the reputation of the provider.
Pillar 5: Data Protection and Confidentiality
Protecting client information is one of the most important considerations in law firm AI governance.
Model Rule 1.6 generally protects information relating to the representation, subject to applicable authorizations and exceptions.
That duty is broader than the evidentiary attorney-client privilege, which is governed by separate legal principles.
AI tools create new information flows, including the potential transmission, processing, storage, and reuse of information through systems operated by third parties.
They can also create risks inside a firm when information becomes accessible to people who should not receive it.
Effective controls begin with understanding those information flows.
Firms should establish procedures for:
- Classifying client and firm information according to sensitivity.
- Determining which categories of information may be used with particular AI platforms.
- Limiting access according to roles, matters, and client restrictions.
- Evaluating storage, retention, training rights, and deletion procedures.
- Documenting appropriate safeguards and responding to suspected exposure.
- Reviewing any client-specific instructions or engagement restrictions affecting AI use.
ABA Formal Opinion 512 provides important guidance on the confidentiality concerns associated with generative AI.
It specifically addresses the risk that certain self-learning systems may disclose information relating to one representation to other users, including users within the same firm.
The opinion concludes that informed consent is required before inputting information relating to a representation into a tool presenting the described disclosure risks.
It also recognizes that not every use of generative AI requires consent. For example, appropriate general brainstorming that does not involve information relating to a representation may not trigger that requirement.
Separately, Rule 1.4 requires a contextual analysis of whether AI use must be disclosed to the client.
Law firms should therefore avoid two oversimplifications: assuming that all third-party AI use automatically waives privilege, or assuming that every AI task always requires advance informed consent.
The applicable professional rules, tool characteristics, client information, contractual arrangements, and facts of the representation matter.
Governance should make those distinctions operational through appropriate approvals and instructions.
A policy that merely prohibits “unsafe AI” provides little help unless attorneys and staff can determine which uses are authorized and what safeguards apply.
Pillar 6: Continuous Oversight and Training
The sixth pillar may be the one most likely to determine whether the other five remain effective.
An AI governance program is not complete when the firm publishes its policy.
Applications change. Vendors revise their terms. Employees join and leave. New use cases emerge. Professional guidance continues to develop.
A control that was appropriate when a tool was approved may require reconsideration after a material change in functionality.
Governance must therefore include continuing oversight.
In my CLE framework, I recommend quarterly governance reviews, with additional review when significant incidents or changes occur.
Quarterly review is a proposed management practice, not a universal interval mandated by the Model Rules.
The appropriate frequency should reflect the firm’s technology, client requirements, and risk exposure.
A governance review might consider:
- Which AI tools remain in active use?
- Have new applications or features appeared?
- Are employees following approved procedures?
- Are outputs receiving the required review?
- Have incidents, errors, or near misses occurred?
- Have vendor or legal requirements changed?
- Does the firm need additional training?
Training should be proportional to the employee’s responsibilities.
An attorney preparing a court filing needs to understand source verification, legal accuracy, and the independent judgment required before submission.
An intake employee using approved automation may need instruction about confidentiality, permissible representations, escalation, and limits on automated responses.
A governance lead may need additional knowledge about vendor evaluation, records, and incident response.
“Governance is how you operationalize trust internally and externally.”
Jeff Howell, Esq. | Lex Wire Journal
The purpose is not to guarantee that errors will never occur.
It is to create an organization better equipped to prevent foreseeable problems, identify failures, respond appropriately, and improve.
Turning the Six Pillars Into an Operational System
Understanding the six pillars is only the beginning.
The real test is whether a firm can translate them into a governance process that functions during ordinary legal work.
In my CLE programs, I organize implementation into four phases: foundation, policy and training, integration, and continuous improvement.
These phases are intended to be practical and scalable rather than administratively burdensome.
Foundation
Designate a governance lead and conduct an inventory of AI use throughout the firm.
Identify approved applications, unapproved experimentation, existing safeguards, and the most consequential risk gaps.
Establish a short statement of the firm’s purpose for adopting AI, connected to client service, confidentiality, and professional responsibility.
Policy and Training
Publish a clear acceptable-use framework identifying approved tools, authorized tasks, information restrictions, review requirements, and reporting procedures.
Train attorneys and staff on the procedures that apply to their roles. Include AI responsibilities in onboarding and appropriate continuing education.
Integration
Embed vendor evaluation, risk classification, documentation, and human review into normal workflows.
Establish a governance register identifying approved systems, relevant restrictions, responsible personnel, and review procedures.
Use matter-level records where appropriate, with retention and access rules that account for confidentiality and privilege.
Monitoring and Continuous Improvement
Review AI use, policy compliance, vendor changes, incidents, and lessons learned.
Update approved tools and procedures when circumstances change. Conduct periodic training and reassess whether controls remain proportionate to risk.
Consider a hypothetical ten-attorney firm with no formal AI governance system.
The managing partner could begin by meeting with attorneys and staff to identify which AI applications are actually being used.
That inventory might reveal several legitimate applications along with unapproved tools handling information they should not receive.
The firm could then assign a governance lead, prepare an approved tools list, establish basic data restrictions, and define the review required for legal work.
New applications would pass through a documented vendor and risk review. Staff would receive appropriate training, and the firm would establish a regular schedule for reviewing its procedures.
None of this necessarily requires purchasing an elaborate new software platform.
A small firm might maintain its approved tools register and governance documentation in existing secured systems.
The important objective is consistency.
“AI governance is a workflow, not a whitepaper.”
Jeff Howell, Esq. | Lex Wire Journal
That is the dividing line between having a policy and operating a governance system.
Measuring Law Firm AI Governance Maturity
Governance should evolve as the firm’s understanding and use of AI develops.
I describe that progression through a four-stage maturity model.
| Stage | Characteristics | Next Priority |
|---|---|---|
| Reactive | Informal experimentation, limited visibility, inconsistent procedures. | Establish ownership and inventory existing use. |
| Controlled | Approved tools, baseline policies, and initial training. | Integrate risk classification and verification into workflows. |
| Integrated | Routine vendor review, documented oversight, consistent escalation. | Measure whether controls actually work. |
| Optimized | Regular measurement, feedback, updates, and continuous improvement. | Refine governance as tools, risks, and practices evolve. |
The model is a management framework, not an official professional responsibility classification.
Firms can track indicators such as the proportion of active tools that have undergone approval, completion of relevant training, documented review of high-risk work, vendor reassessments, and identified incidents.
However, the presence of documentation is not proof that a system is effective.
A low number of reported incidents might indicate good controls, or it might indicate that employees are not recognizing and reporting problems.
Likewise, completing an AI training module does not necessarily demonstrate competence.
Governance maturity should be assessed through both documented procedures and evidence that those procedures influence actual conduct.
Governance as the Architecture of Operational Trust
The practical objective of AI governance is broader than avoiding disciplinary exposure or satisfying a vendor procurement checklist.
A functioning framework creates clarity for the people who use AI, for the clients whose matters may be affected, and for the leadership responsible for overseeing the practice.
Attorneys and staff know which applications are permitted.
Supervising lawyers know what review must occur before relying on AI-assisted work.
Clients can receive accurate explanations of the firm’s technology practices when communication is appropriate or required.
Management has a system for understanding what is being used, how decisions are made, and what happens when something goes wrong.
None of that eliminates risk.
But it replaces informal assumptions with identifiable responsibilities and repeatable procedures.
The NIST AI Risk Management Framework provides a useful voluntary reference for this broader approach.
Its functions of governing, mapping, measuring, and managing AI risk reinforce the importance of integrating risk management across an organization’s activities.
NIST’s framework does not replace the professional rules governing attorneys. It can, however, help organize the operational processes through which those obligations are addressed.
Ultimately, law firms should understand AI governance as a law practice management function, not simply a technology compliance exercise.
The Bottom Line: AI Governance Must Become How the Firm Operates
The question facing law firms is no longer whether artificial intelligence will become part of legal work.
For many firms, it already has.
The more important question is whether leadership can establish clear responsibility for how those technologies are selected, used, supervised, and evaluated.
The six pillars provide the necessary structure: leadership, policy design, risk classification, vendor evaluation, data protection, and continuous oversight.
The four implementation phases translate that structure into ordinary operations.
The maturity model helps firms evaluate whether their governance capabilities are improving.
None of these elements replaces professional judgment.
They create a more reliable environment in which lawyers can exercise that judgment while using increasingly capable technology.
A firm does not become responsibly governed because it possesses an AI policy.
It becomes responsibly governed when its people understand their duties, follow appropriate procedures, and remain accountable for the results.
“Governance isn’t a brake pedal; it’s the steering wheel for incorporating AI into your practice.”
Jeff Howell, Esq. | Lex Wire Journal
That is the objective: not to resist technological progress, but to ensure that innovation proceeds through a framework of professional responsibility, operational discipline, and human accountability.
AI governance works when it becomes part of how the law firm practices law.
Related Lex Wire Journal Analysis
This article focuses on the operational systems through which law firms govern AI. It complements, rather than duplicates, Lex Wire’s broader analysis of institutional intelligence and technology control.
- Building Your Law Firm’s AI Playbook provides a concise companion on practical policies, procedures, and implementation.
- Who Controls Your Law Firm’s AI Intelligence Layer? examines the development of institutional intelligence, technology dependency, and long-term governance.
- AI Bias, Ethics, and Risk Management for Law Firms explores specialized risk considerations that may arise within AI-assisted work.
Authorities and Source Materials
Professional Responsibility
- American Bar Association, Formal Opinion 512, Generative Artificial Intelligence Tools (July 29, 2024).
- American Bar Association, Model Rules of Professional Conduct , including Rules 1.1, 1.4, 1.6, 3.1, 3.3, 5.1, and 5.3.
Risk Management Frameworks
- National Institute of Standards and Technology, AI Risk Management Framework , including AI RMF 1.0 and accompanying resources.
CLE Source Programs
- Jeff Howell, Esq., Building an AI Governance Framework for Your Law Firm: Policies, Procedures, and Ongoing Compliance , National Academy of Continuing Legal Education.
- Jeff Howell, Esq., AI Governance in Law Firms: Policies, Audits, and Risk Management , Lawline.